Nine ModiLoader phishing campaigns detected in May 2024 targeting SMBs. Deployed three sets of infostealers: Rescoms, Agent Tesla, and Formbook, to not only spread malicious emails, but also host malware and steal data
Researchers of ESET, a global European leader in the cybersecurity market, investigated nine widely spread phishing campaigns targeting small and medium-sized businesses (SMEs) in Poland, Romania and Italy in May 2024, through which several families of malware were distributed. Compared to the previous year, attackers have abandoned AceCryptor in favor of ModiLoader as the main malware distribution tool, and have also expanded the malware they use. The attackers used previously compromised email accounts and company servers to not only spread malicious emails, but also host malware and collect stolen data. In May 2024 alone, ESET solutions protected over 26,000 users – including over 21,000 (80%) in Poland – against these threats.
“In total, we recorded nine phishing campaigns, seven of which targeted Poland throughout the month of May,” explains Jakub Kaloč, who analyzed the campaigns. “The final payload that was distributed and launched on compromised computers varied; we detected campaigns that distributed the infostealer Formbook; the remote access and infostealer trojan Agent Tesla; and Rescoms RAT, a remote control and surveillance software capable of stealing sensitive information,” he adds.
In general, all campaigns followed the same pattern. The target companies received an email with a commercial offer. As in the phishing campaigns of the second half of 2023, the attackers impersonated existing companies and their employees, a technique that helps increase the success rate of campaigns. This way, even if the potential victim was looking for typical red flags (as well as possible translation errors), these were absent and the email appeared completely legitimate.
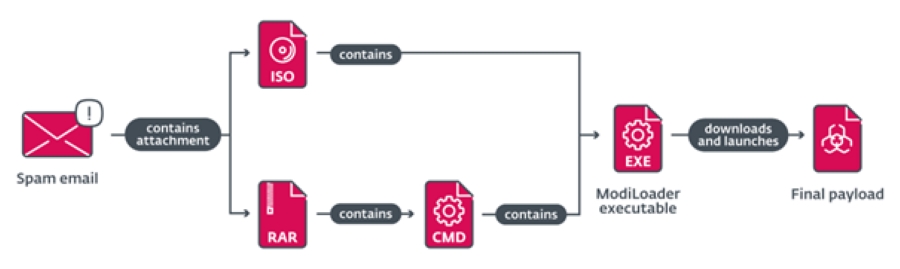
Emails from all campaigns contained a malicious attachment that the potential victim was incentivized to open. The file itself was an ISO file or archive containing the ModiLoader executable, a Delphi downloader with a simple task: download and launch malware. In two of the campaigns, ModiLoader samples were configured to later download malware from a compromised server belonging to a Hungarian company. In other campaigns, ModiLoader downloaded subsequent malware from Microsoft's OneDrive cloud storage service.
More information on ModiLoader campaigns, on the blog “Phishing targeting Polish SMBs continues via ModiLoader” su WeLiveSecurity-com. Follow ESET Research on Twitter (now known as X) For the latest news from ESET Research.